Best Exposure Management Platforms - Page 2

Last updated: November 18, 2026

How Many Exposure Management Platforms Products Does G2 Track?

Total Products under this Category: 81

Category Stats (Nov 2026)

  • Average Rating: 4.67/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Topscan (+0.59%) - Among all products in this category, Topscan recorded the largest rating increase compared to last month

Last updated: November 17, 2026

How Does G2 Rank Exposure Management Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,000+ Authentic Reviews
  • 81+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

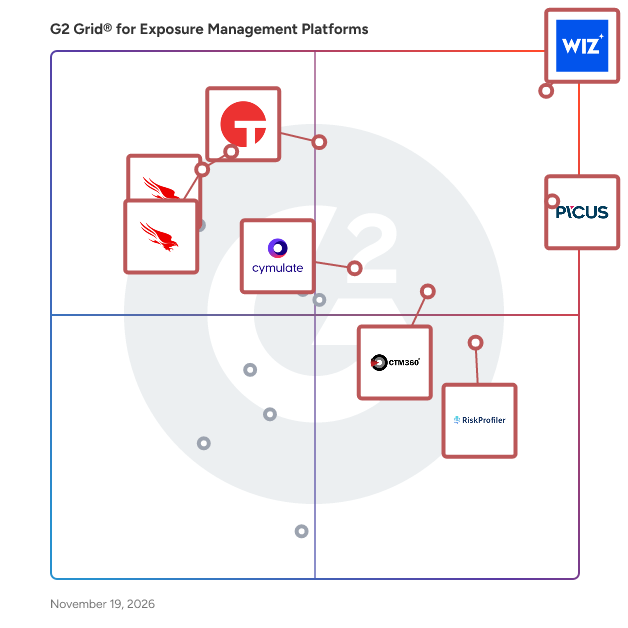
G2 Grid® for Exposure Management Platforms

G2 Grid® for Exposure Management Platforms plotting products by satisfaction and market presence

Highlighted products: Wiz, Picus Security, Tanium, CTM360, RiskProfiler - External Threat Exposure Management, Cymulate, CrowdStrike Falcon Cloud Security, and CrowdStrike Falcon Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/exposure-management-platforms/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=picus-security&focus%5B%5D=tanium&focus%5B%5D=ctm360-ctm360&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=cymulate&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=crowdstrike-falcon-exposure-management)

Strobes Security

Strobes is an AI-driven exposure management platform designed to help organizations streamline their security operations by unifying various security methodologies, including Attack Surface Management (ASM), Application Security Posture Management (ASPM), Risk-Based Vulnerability Management (RBVM), and Penetration Testing as a Service (PTaaS). This comprehensive solution provides users with a holistic view of their security posture, enabling them to identify, assess, and respond to potential risks and vulnerabilities effectively. Targeted primarily at security teams and IT professionals, Strobes caters to organizations of all sizes that require a robust approach to managing their security exposure. The platform is particularly beneficial for those who need to navigate the complexities of modern security environments, where multiple tools and processes can lead to fragmented insights. By consolidating various security functions into a single workflow, Strobes empowers users to make informed decisions based on a complete understanding of their risk landscape. One of the key features of Strobes is its extensive integration capabilities, boasting over 120 integrations with existing security tools and systems. This allows organizations to pull findings from disparate sources into a single view, enriching data with contextual information that enhances the relevance of insights. The platform's advanced correlation capabilities help identify relationships between different vulnerabilities and risks, enabling security teams to prioritize their remediation efforts effectively. The user-friendly dashboards in Strobes serve as a central hub for monitoring security activities, encompassing everything from asset discovery and vulnerability insights to Service Level Agreement (SLA) tracking and ticketing. This comprehensive visibility supports continuous prioritization and fix validation, allowing teams to address the most critical issues first. By automating triage processes, Strobes ensures that real risks and exposures are highlighted, facilitating a more efficient response to potential threats. Overall, Strobes stands out in the exposure management landscape by providing a cohesive and intelligent approach to security management. Its ability to unify various methodologies, coupled with powerful automation and integration features, positions it as a valuable tool for organizations seeking to enhance their security posture and effectively manage their exposure to risks.

Average Rating: 4.5/5.0

Total Reviews: 44

Who Is the Company Behind Strobes Security?

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 42% Medium, 33% Large

What Do G2 Reviewers Say About Strobes Security?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid vulnerability assessments that enhance security fixes significantly, boosting efficiency and prioritization.
  • Users appreciate the rapid vulnerability assessments and prioritized remediation that enhance their security processes significantly.
  • Users value the thorough security measures of Strobes Security, impressed by its attention to detail in vulnerability management.
  • Users value the responsive customer support of Strobes Security, enhancing the experience with timely and effective assistance.
  • Users find Strobes Security exceptionally easy to use, enjoying quick setup and intuitive dashboards for efficient workflows.
Cons
  • Users express dissatisfaction with the inadequate reporting in Strobes Security, citing lack of transparency and customization options.
  • Users find the limited customization options in Strobes Security hinder initial workflow setup and usability improvements.
  • Users find Strobes Security's poor usability challenging initially, with a steep learning curve and complex dashboard navigation.
  • Users find the reporting issues in Strobes Security limit transparency and hinder customization for effective analysis.
  • Users find the user interface complex, making initial customization and workflow setup a challenging experience.

What Are Recent G2 Reviews of Strobes Security?

vRx by Vicarius

vRx by Vicarius goes beyond patch management to offer the most advanced vulnerability remediation solution in the market. vRx offers 3 built-in methods to keep you covered at all times: 1) Automated Patching: vRx catalogs all your apps and finds the patches they need, and applies them - automatically and on the schedule or frequency of your choosing. 2) Scripting: For more complex vulnerabilities or configuration based vulnerabilities, vRx includes a fully fledged scripting engine. 3) Patchless Protection: x_protect or patchless protection is a compensating control that reduces the risk of an affected app even when a patch is not yet developed or cannot be deployed vRx helps 500+ customers across 50 countries find AND immediately remediate vulns that impact their business.

Average Rating: 4.9/5.0

Total Reviews: 62

Who Is the Company Behind vRx by Vicarius?

  • Seller: Vicarius
  • Company Website:
  • Year Founded: 2016
  • HQ Location: New York, New York
  • LinkedIn® Page: www.linkedin.com
    100 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Medium, 33% Small

What Do G2 Reviewers Say About vRx by Vicarius?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive interface of vRx by Vicarius, making task management straightforward and streamlined.
  • Users appreciate the high level of automation in vRx, enabling efficient vulnerability management from detection to remediation.
  • Users greatly value the ease of patch management with vRx, simplifying operations and enhancing security effectively.
  • Users value the effective vulnerability identification of vRx by Vicarius, streamlining both detection and remediation processes.
  • Users appreciate the intuitive interface of vRx by Vicarius, enhancing task management and real-time visibility.
Cons
  • Users note the missing features in vRx, particularly the lack of network scanning and automated asset grouping.
  • Users note the need for inadequate reporting, highlighting limited customization and absence of compliance reports in vRx.
  • Users find complexity in integration and advanced analytics of vRx challenging, complicating effective use for non-technical users.
  • Users note dashboard issues that hinder customization and adaptation for different audiences in vRx.
  • Users find inaccurate information in vRx, leading to confusion and a lack of compliance reports for effective management.

What Are Recent G2 Reviews of vRx by Vicarius?

What Are G2 Users Discussing About vRx by Vicarius?

ResilientX Security Platform

ResilientX Unified Exposure Management Platform is the leading platform that unifies Attack Surface Management, Web Application Security Testing, Network Security Testing, Cloud Security Posture Management, and Third-Party Risk Management.

Average Rating: 5.0/5.0

Total Reviews: 17

Who Is the Company Behind ResilientX Security Platform?

Who Uses This Product?

  • Company Size: 47% Medium, 35% Small

What Do G2 Reviewers Say About ResilientX Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the excellent security management provided by ResilientX, ensuring compliance and support for their needs.
  • Users value the prompt vulnerability detection by ResilientX, enhancing security and providing timely alerts for system protection.
  • Users value the prompt alerts for detected attacks and the comprehensive vulnerability updates from ResilientX.
  • Users value the exceptional customer support from ResilientX, who are always ready to assist with expertise.
  • Users value the prompt alerts for detected attacks and actionable recommendations provided by ResilientX Security Platform.
Cons
  • Users find the complex setup of ResilientX challenging, wishing for easier onboarding and more customizable options.
  • Users find the difficult customization of ResilientX's platform limits usability for non-technical stakeholders and onboarding is cumbersome.
  • Users find the difficult initial setup of ResilientX Security Platform to be challenging and in need of improvement.
  • Users desire improved integration with existing SIEM systems to enhance the efficiency of their security operations.
  • Users find the platform robust but desire more integration with existing SIEM systems to enhance their security operations.

What Are Recent G2 Reviews of ResilientX Security Platform?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

AI-Native Continuous Offensive Security Platform

RidgeBot by Ridge Security is an AI-powered platform for continuous security validation that enables CISOs to minimize cyber risks from increasingly sophisticated and frequent cyberattacks by validating the cybersecurity posture and controls that protect attack surfaces. RidgeBot delivers continuous threat exposure management by automatically testing an organization’s entire Internet Protocol (IP)-based attack surfaces, including network infrastructure, applications, websites, IoT, and OT. RidgeBot pinpoints the most critical vulnerabilities using ethical hacking techniques. RidgeBot’s dynamic AI-powered decision-making capability supports many use cases, including DevSecOps, compliance, incident response verification, and custom attack simulations. RidgeBot maintains a library of over 36,000 plugins to launch complex penetration tests and attack simulations, with detailed reporting of results and remediation recommendation.

Average Rating: 4.5/5.0

Total Reviews: 98

Who Is the Company Behind AI-Native Continuous Offensive Security Platform?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Small, 45% Medium

What Do G2 Reviewers Say About AI-Native Continuous Offensive Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the automation features of RidgeBot, which efficiently streamline security validation and prioritization of threats.
  • Users find the ease of use exceptional, praising its intuitive interface and straightforward setup for security tasks.
  • Users appreciate the efficiency of automated pentesting with RidgeBot, significantly reducing manual validation and saving time.
  • Users value the autonomous vulnerability testing of RidgeBot, significantly enhancing efficiency and risk assessment in security processes.
  • Users appreciate the efficiency of RidgeBot in automating penetration testing and prioritizing critical vulnerabilities effectively.
Cons
  • Users find the platform's setup to be complex and challenging, especially in customized or legacy environments.
  • Users find the complex setup of the AI-Native platform challenging, particularly for newcomers and unique environments.
  • Users feel there are several missing features, like improved API testing and custom reporting templates for compliance.
  • Users find the customer support lacking, often leaving them to troubleshoot issues independently.
  • Users find the poor documentation challenging, making initial setup and troubleshooting difficult, especially for new admins.

What Are Recent G2 Reviews of AI-Native Continuous Offensive Security Platform?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, enjoying its user-friendly interface and convenient access to essential information.
  • Users value the near false positive free vulnerability scanning of Edgescan, making web application testing efficient and reliable.
  • Users highly value the fantastic customer support from Edgescan, enhancing their overall experience significantly.
  • Users value the validated, near false positive free vulnerability scanning of Edgescan, enhancing their testing experience significantly.
  • Users appreciate the user-friendly console of Edgescan, as it offers easy access and comprehensive functionality for managing vulnerabilities.
Cons
  • Users find the complex UI of Edgescan challenging, leading to inefficiencies and difficulties in task navigation.
  • Users find the limited customization for hosts and filtering frustrating, impacting their ability to adapt to changes.
  • Users find the poor interface design of Edgescan frustrating, hindering efficient navigation and task completion.
  • Users experience slow performance with Edgescan, as scans can take longer due to thorough validation processes.
  • Users find the user interface challenging to navigate, leading to delays and difficulty performing common tasks.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?

Microsoft Security Exposure Management

Microsoft Security Exposure Management is a comprehensive security solution designed to provide organizations with unified visibility into their security posture across various assets and workloads. By continuously discovering and assessing assets, it enables security teams to proactively identify vulnerabilities, prioritize critical risks, and implement effective remediation strategies to reduce the attack surface and enhance overall security. Key Features and Functionality: - Attack Surface Management: Offers a continuous and comprehensive view of the organization's attack surface, allowing teams to monitor exposure and focus on protecting critical assets. - Attack Path Analysis: Visualizes potential attack paths, enabling security teams to identify and prioritize remediation efforts to reduce risks effectively. - Unified Exposure Insights: Aggregates security posture data from various sources, providing decision-makers with a consolidated view of the organization's threat exposure to facilitate informed decision-making. - Integration with Security Tools: Seamlessly integrates with both Microsoft and non-Microsoft security and infrastructure tools, including Microsoft Defender for Endpoint, Microsoft Defender for Identity, and Microsoft Defender for Cloud Apps, to provide a holistic view of the security environment. Primary Value and Problem Solved: Microsoft Security Exposure Management addresses the challenge of fragmented security data and siloed management by unifying disparate data sources into a single, comprehensive view. This integration empowers organizations to proactively manage their attack surfaces, protect critical assets, and mitigate exposure risks. By providing continuous visibility and actionable insights, it enables security teams to transition from reactive vulnerability management to a proactive, risk-based approach, thereby enhancing the organization's overall security posture and resilience against evolving cyber threats.

Average Rating: 4.4/5.0

Total Reviews: 9

Who Is the Company Behind Microsoft Security Exposure Management?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Company Size: 50% Medium, 40% Large

What Are Recent G2 Reviews of Microsoft Security Exposure Management?

Bitsight

Bitsight is the global leader in cyber risk intelligence, leveraging advanced AI to empower organizations with precise insights derived from the industry’s most extensive external cybersecurity dataset. With more than 3,500 customers and over 68,000 organizations active on its platform, Bitsight delivers real-time visibility into cyber risk and threat exposure, enabling teams to rapidly identify vulnerabilities, detect emerging threats, prioritize remediation, and mitigate risks across their extended attack surface. Bitsight proactively uncovers security gaps across infrastructure, cloud environments, digital identities, and third- and fourth-party ecosystems. From security operations and governance teams to executive boardrooms, Bitsight provides the unified intelligence backbone required to confidently manage cyber risk and address exposures before they impact performance.

Average Rating: 4.5/5.0

Total Reviews: 76

Who Is the Company Behind Bitsight?

  • Seller: Bitsight
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    694 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Hospital & Health Care
  • Company Size: 71% Large, 24% Medium

What Do G2 Reviewers Say About Bitsight?

AI-generated summary from verified user reviews

Pros
  • Users value the simple daily security score from BitSight, providing clear insights into cyber risk management.
  • Users appreciate the simple daily "security score" for cyber risk, enhancing safety and risk management easily.
  • Users appreciate the ease of use of BitSight, finding it straightforward and user-friendly for managing security risks.
  • Users value the powerful insights from BitSight's AI features and comprehensive risk monitoring capabilities.
  • Users commend the responsive customer support of Bitsight, ensuring quick assistance and effective use of the platform.
Cons
  • Users express concerns about missing features in Bitsight, particularly regarding transparency and proactive remediation management.
  • Users are frustrated by the lack of clarity in Bitsight's scoring mechanism and accuracy of findings.
  • Users experience poor notifications from Bitsight, with alerts being untimely and often missing critical information.
  • Users experience slow performance with Bitsight, facing lag and delayed updates on remediation efforts and scores.
  • Users report delay issues with BitSight's response times and vulnerability updates, impacting their overall experience.

What Are Recent G2 Reviews of Bitsight?

What Are G2 Users Discussing About Bitsight?

UncommonX

UncommonX is an AI-powered Exposure Management platform that gives security teams a single view of their entire environment, ranks risk by what actually matters to the business, and tells them what to fix and in what order. Recognized for 2025 as one of Crain's Most Innovative Companies in Chicago, UncommonX is built on a single promise: See everything. Miss nothing. What makes the platform distinct is its architecture. UncommonX is agentless, which means it sees devices and systems other security tools cannot, including OT, IoT, third-party applications, and shadow IT. It is also vendor-agnostic, with 300+ integrations across the EDR, firewall, email security, and other tools customers already run. Where most security AI is built around detection, UncommonX uses AI to score every exposure against NIST CSF and rank what matters most, so teams spend their time fixing rather than triaging. UncommonX serves private companies across manufacturing, healthcare, financial services, hospitality, and professional services. These are organizations with multi-site operations, lean security teams, and a need to consolidate tools rather than add to them. Customers have reported $200K+ in real savings through tool consolidation on the UncommonX platform. The platform is backed by 26 US patents in Exposure Management and AI, with 100% US-based security operations and development. UncommonX is also a member of the NVIDIA Inception Program, supporting its work in applying AI to cybersecurity at scale. Headquartered in Chicago, UncommonX gives security leaders the visibility, intelligence, and speed they need to see across their entire environment and act on what matters most. To learn more, visit www.uncommonx.com.

Average Rating: 4.8/5.0

Total Reviews: 11

Who Is the Company Behind UncommonX?

  • Seller: UncommonX
  • Company Website:
  • Year Founded: 2012
  • HQ Location: Chicago, US
  • LinkedIn® Page: www.linkedin.com
    24 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 64% Medium, 18% Large

What Do G2 Reviewers Say About UncommonX?

AI-generated summary from verified user reviews

Pros
  • Users value the expertise and responsiveness of UncommonX, enhancing clarity and control in compliance management.
  • Users commend the excellent customer support of UncommonX, highlighting their responsiveness and personalized service.
  • Users value the 24/7 support availability of UncommonX, ensuring peace of mind with real-time assistance and regular check-ins.
  • Users praise the expertise and responsiveness of UncommonX's team, ensuring effective security management and support.
  • Users value the effective threat detection of UncommonX, enabling quick responses to potential security incidents with confidence.
Cons
  • Users experience communication issues with UncommonX, wishing for faster responses to potential concerns.
  • Users find response times for reporting issues less than ideal, wishing for quicker resolutions to potential problems.
  • Users feel that UncommonX has slow performance in response times, making timely issue resolution a bit challenging.

What Are Recent G2 Reviews of UncommonX?

Topscan

Topscan is a continuous security monitoring platform for the DevOps engineer or CTO who owns security among other things. It covers the whole delivery pipeline in one subscription — static analysis in your code, dynamic scanning of live applications and infrastructure, and continuous monitoring of everything you expose to the internet — instead of three separate vendors for SAST, DAST and attack surface management. Perimeter. External infrastructure scanning reports open ports, service versions and known server vulnerabilities matched against CVE databases, with unlimited scheduled rescans. Asset discovery maps the subdomains and hosts you forgot about — the Grafana, the Sentry, the staging box nobody remembers deploying — and new hosts arrive with a review prompt: you confirm ownership before anything is scanned. Attack surface monitoring keeps every exposed service inventoried, and certificate watch catches TLS/SSL expiry weeks early instead of on the Friday night it happens. Applications and code. Web application scanning runs OWASP-class checks against live apps: SQL injection, XSS, exposed admin panels, default credentials, missing headers. Static application security testing covers three kinds of risk in one scan — vulnerable code patterns, committed secrets and keys, and known CVEs in dependencies (software composition analysis) — on every commit, pointing at the exact file and line. Pipeline and cloud. A CI/CD webhook gives you a unique event link to call from the last step of your deploy script: no API keys, no agent, nothing installed on your servers. AWS connects with keys you issue to discover EC2 and Route 53 resources, which are added to monitoring and rescanned when they change. Workflow. Findings are deduplicated and carry severity in your context, CVSS, a first-seen date and an SLA clock with overdue flags. Snooze what you accept, mark false positives and they stop resurfacing, and work through a large backlog in triage mode. Informational findings stay out of the feed and never touch your score. One security score tracks the whole estate over time — the number you show yourself, your CEO or an auditor. Alerts reach the team in Slack or Microsoft Teams and turn into Jira tickets; chat and tracker routing starts on the Advanced plan. Audit and compliance. Auditors ask for evidence of regular scanning and an inventory of what is exposed: scan history with downloadable reports and an exportable asset inventory answer both, which is what most teams use Topscan for ahead of SOC 2, ISO 27001 or a customer security review. Auditor seats are free and read-only, and users are unlimited on every plan. Pricing starts at $129 per month and is published on the site — no demo call required to see it — with a 14-day free trial of the full plan and no credit card. Add a domain and the first map of your perimeter arrives in five to ten minutes.

Average Rating: 4.9/5.0

Total Reviews: 7

Who Is the Company Behind Topscan?

  • Seller: Topscan
  • Year Founded: 2024
  • HQ Location: Dubai, AE
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 71% Small, 29% Medium

What Are Recent G2 Reviews of Topscan?

Saner CVEM

Prevention-first Vulnerability and Exposure Management for unified visibility, prioritization, compliance, and remediation Saner Continuous Vulnerability and Exposure Management unifies asset exposure, posture anomaly detection, vulnerability assessment, compliance management, risk prioritization, patching, and endpoint actions in one dashboard. Saner CVEM is built to help teams continuously detect, assess, prioritize, and remediate vulnerabilities and other security risks from a unified console Why Choose Saner CVEM? • Unified dashboard with interactive views across visibility, detection, prioritization, and remediation for a single source of truth • Complete asset visibility across endpoint and non-endpoint devices, operating system applications, third-party applications, and lifecycle changes • Continuous risk discovery with rapid scans, daily-updated risk intelligence, and posture anomaly detection that helps surface outliers and misconfigurations faster • Context-driven prioritization with SSVC categories such as Act, Attend, Track, and Track* so teams can focus on the risks that deserve action first. • Continuous compliance management with built-in templates, customizable profiles, daily checks, and deviation tracking across common frameworks. • Integrated patching and remediation with vulnerability-to-patch mapping, automated deployment workflows, and endpoint actions from the same ecosystem. • Machine-learning-assisted analysis to identify deeper risk patterns, detect unusual posture, and support smarter remediation decisions. • Customizable, audit-ready reporting for security, IT, and compliance teams that need clearer evidence and easier tracking. • Flexible deployment on cloud or on-premises, with remediation support across Windows, Linux, macOS, and AIX environments.

Average Rating: 4.5/5.0

Total Reviews: 72

Who Is the Company Behind Saner CVEM?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Small, 38% Medium

What Do G2 Reviewers Say About Saner CVEM?

AI-generated summary from verified user reviews

Pros
  • Users value the robust security features of Saner CVEM for effective endpoint management and vulnerability assessments.
  • Users appreciate the rich feature set of Saner CVEM, streamlining security management and enhancing vulnerability assessments efficiently.
  • Users commend the ease of use of Saner CVEM, allowing swift deployment and seamless management across diverse systems.
  • Users commend the exceptional customer support of Saner CVEM, providing assistance during critical deployments and compliance setups.
  • Users value the efficient compliance management of Saner CVEM, facilitating seamless audit preparation and vulnerability tracking.
Cons
  • Users note significant integration issues with Saner CVEM, requiring workarounds for smooth multi-tenant management and legacy software connections.
  • Users find the pricing structure expensive for small organizations, impacting their decision to choose Saner CVEM.
  • Users find the limited features of Saner CVEM restrict effective multi-tenant support and integration capabilities.
  • Users experience slow performance during initial loading and installation, impacting daily checks and onboarding efficiency.
  • Users experience slow scanning during initial dashboard loads and installation, affecting efficiency with large data sets.

What Are Recent G2 Reviews of Saner CVEM?

What Are G2 Users Discussing About Saner CVEM?

ArmorCode Unified Exposure Management

ArmorCode is redefining security governance in the AI era as the agentic control plane for Unified Exposure Management. Its Platform delivers software and infrastructure security governance that consolidates findings and prioritizes ones with real business impact, surfaces exploitability and attack paths, de-risks AI adoption, and accelerates compliance. ArmorCode's Agentic Control Plane helps enterprises manage security risk across today's heterogeneous environments. Powered by 
Anya Agents, an agentic workforce for enterprise security, it connects a Context Risk Graph to 400+ sources; unifying exposure management across infrastructure, software supply chains, applications, and AI systems; and delivering visibility, insight, and control without replacing existing tools. ArmorCode was founded in 2020 by Nikhil Gupta and is headquartered in Palo Alto, California. Trusted by dozens of Fortune 1000 enterprise customers, ArmorCode serves North America and EMEA with a team of 200+ employees.

Average Rating: 4.1/5.0

Total Reviews: 4

Who Is the Company Behind ArmorCode Unified Exposure Management?

  • Seller: ArmorCode
  • Year Founded: 2020
  • HQ Location: Palo Alto, California, United States
  • LinkedIn® Page: www.linkedin.com
    222 employees on LinkedIn®
  • Ownership: Dana Torgersen

Who Uses This Product?

  • Company Size: 50% Medium, 25% Large

What Do G2 Reviewers Say About ArmorCode Unified Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users value the enhanced security and streamlined vulnerability management provided by ArmorCode, boosting their overall efficiency.
  • Users value the enhanced security in ArmorCode, effectively managing vulnerabilities from development to deployment.
  • Users commend ArmorCode for its effective vulnerability identification, streamlining workflows and enhancing security throughout development and deployment.
  • Users value the automation features of ArmorCode for effortlessly enhancing security from development to deployment.
  • Users value the centralization of vulnerabilities in ArmorCode, enhancing workflows for security teams effectively.
Cons
  • Users find that ArmorCode requires improvement in scalability and customization for better data presentation and analysis.
  • Users find the reporting inadequate, noting accuracy issues and limited customization options in ArmorCode Unified Exposure Management.
  • Users find that the data presentation requires significant effort to clearly convey organizational risks effectively.
  • Users find the information overload from ArmorCode challenging, requiring significant effort to distill actionable insights.
  • Users note the limited customization options in reporting, leading to inaccuracies and less tailored insights.

What Are Recent G2 Reviews of ArmorCode Unified Exposure Management?

SentinelOne Singularity Cloud Security

Singularity Cloud Security is SentinelOne’s comprehensive, cloud-native application protection platform (CNAPP). It combines the best of agentless insights with AI-powered threat protection, to secure and protect your multi-cloud infrastructure, services, and containers from build time to runtime. SentinelOne’s CNAPP applies an attacker’s mindset to help security practitioners better prioritize their remediation tasks with evidence-backed Verified Exploit Paths™. The efficient and scalable runtime protection, proven over 5 years and trusted by many of the world’s leading cloud enterprises, harnesses local, autonomous AI engines to detect and thwart runtime threats in real-time. CNAPP data and workload telemetry is recorded to SentinelOne’s unified security lake, for easy access and investigation.

Average Rating: 4.9/5.0

Total Reviews: 122

Who Is the Company Behind SentinelOne Singularity Cloud Security?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About SentinelOne Singularity Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the strong AI-driven threat detection of SentinelOne Singularity, enhancing security while reducing manual efforts.
  • Users appreciate the ease of use of SentinelOne Singularity Cloud Security, praising its intuitive implementation and management.
  • Users appreciate the effective vulnerability detection of SentinelOne, enabling faster responses and enhanced security posture.
  • Users value the real-time protection of SentinelOne for securing cloud servers and data, enhancing overall security posture.
  • Users value the strong AI-driven threat detection in SentinelOne Singularity Cloud Security, enhancing efficiency and response times.
Cons
  • Users find the complexity of setup and configuration in SentinelOne Singularity Cloud Security challenging and time-consuming.
  • Users find that ineffective alerts necessitate careful tuning, which can complicate their experience with SentinelOne Singularity Cloud Security.
  • Users find the initial setup complex and time-consuming, which can challenge teams lacking cloud security expertise.
  • Users find the difficult configuration of SentinelOne Singularity Cloud Security can be complex and time-consuming initially.
  • Users find the poor UI of SentinelOne Singularity Cloud Security to be clunky, complicating navigation and usability.

What Are Recent G2 Reviews of SentinelOne Singularity Cloud Security?

PlexTrac

PlexTrac is the leading AI-powered platform for pentest reporting and threat exposure management, trusted by Fortune 500 companies and top security providers. Built to help cybersecurity teams continuously manage and reduce threat exposure, PlexTrac centralizes security data, streamlines reporting, prioritizes risk, and automates remediation workflows—empowering teams to drive measurable risk reduction. The platform is ideal for enterprises & service providers looking to deliver a Continuous Threat Exposure Management (CTEM) framework across their business. With our suite of solutions, you can consolidate security data from tools and manual testing, automatically prioritize risks based on business impact, and automate remediation and retesting workflows for ongoing, more effective threat management.

Average Rating: 4.8/5.0

Total Reviews: 15

Who Is the Company Behind PlexTrac?

  • Seller: PlexTrac
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Boise, Idaho
  • LinkedIn® Page: www.linkedin.com
    80 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Consulting
  • Company Size: 40% Large, 40% Small

What Do G2 Reviewers Say About PlexTrac?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive design and extensive features of PlexTrac, enhancing reporting efficiency and user experience.
  • Users commend the amazing customer support of PlexTrac, noting quick and effective assistance for any issues.
  • Users find PlexTrac to have a clean and intuitive UI, making navigation and reporting significantly easier.
  • Users praise PlexTrac for its reporting efficiency, transforming tedious processes into streamlined, organized workflows for assessments.
  • Users value the seamless integrations with tools like Jira and Tenable that enhance efficiency and reduce manual effort.
Cons
  • Users note some missing features in PlexTrac's on-premise version, affecting functionality compared to SaaS options.
  • Users note some complexity in report formatting, requiring extra effort to achieve the desired presentation.
  • Users find the complex setup of PlexTrac challenging, especially for those new to security tools and automation platforms.
  • Users face a difficult learning curve with PlexTrac, though support is readily available for assistance.
  • Users desire more streamlined reporting options in PlexTrac for improved Threat Hunting and Incident Response plans.

What Are Recent G2 Reviews of PlexTrac?

Evolve Security

Evolve Security's patent pending Darwin Attack® platform is a comprehensive collaboration and management tool designed to help organizations manage their cybersecurity services and reduce risks of successful cyberattacks. The platform serves as a repository for research, vulnerability and attack details, compliance requirements, remediation recommendations, and mitigating controls. It also functions as a security feed, collaboration tool, tracking tool, management platform, and reporting platform. The platform enables organizations to actively manage their security program by providing real-time updates on testing progress and findings, which allows for timely remediation. Darwin Attack® is constantly updated with new information and functionality to ensure that it remains effective and efficient in meeting the needs of Evolve Security's clients.

Average Rating: 4.8/5.0

Total Reviews: 53

Who Is the Company Behind Evolve Security?

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 70% Medium, 21% Small

What Do G2 Reviewers Say About Evolve Security?

AI-generated summary from verified user reviews

Pros
  • Users value the actionable intelligence provided by Evolve Security, enhancing their cybersecurity with clear guidance and insights.
  • Users commend the effective communication from Evolve Security, enhancing collaboration and clarity during the pentesting process.
  • Users find the ease of use of Evolve Security's interface enhances their configuration and testing experience.
  • Users value the vulnerability detection expertise of Evolve Security, enhancing their understanding and response to security issues.
  • Users value the effective vulnerability identification by Evolve Security, enhancing their cybersecurity with clear corrective instructions.

What Are Recent G2 Reviews of Evolve Security?

Guardare Core Platform

Guardare is an AI-powered cybersecurity SaaS platform designed to provide organizations with real-time, risk-based visibility across users, devices, and software. By unifying IT, security protocols, and compliance into a single platform, Guardare eliminates fragmented alerts, offering leaders a consolidated source of truth. This integration brings together risks from cloud, identity, endpoint, and community systems, presenting them in a clear, prioritized manner based on business impact. The result is reduced noise, quicker action, and confidence that critical risks are addressed promptly. Key Features and Functionality: - Unified Exposure Management: Combines various security aspects into a single platform, providing a comprehensive view of potential risks. - AI-Driven Analytics: Utilizes artificial intelligence to analyze data in real-time, ensuring timely identification and prioritization of threats. - Integration with Existing Tools: Seamlessly integrates with current IT, security, and HR tools, enhancing existing security infrastructures without the need for additional resources. - Continuous Asset Mapping: Offers ongoing mapping of assets to maintain up-to-date visibility of the organization's security landscape. - Compliance Management: Assists in achieving and maintaining compliance with industry regulations by providing actionable insights and recommendations. Primary Value and Solutions Provided: Guardare addresses the challenge of fragmented and reactive security processes by offering a unified, proactive approach to cybersecurity. It simplifies complex security and compliance challenges, enabling organizations to guard critical assets, mitigate risks, and ensure compliance with industry regulations. By providing a centralized, intelligent dashboard, Guardare empowers IT leaders and their teams to transform complex security processes into clear, confident strategies, optimizing their security posture without the need for additional tools or specialized infosec experience.

Average Rating: 5.0/5.0

Total Reviews: 2

Who Is the Company Behind Guardare Core Platform?

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of Guardare Core Platform?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller