Best Dynamic Application Security Testing (DAST) Software - Page 7

How Many Dynamic Application Security Testing (DAST) Software Products Does G2 Track?

Total Products under this Category: 102

Category Stats (Oct 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: HCL AppScan (+0.24%) - Among all products in this category, HCL AppScan recorded the largest rating increase compared to last month

Last updated: October 24, 2026

How Does G2 Rank Dynamic Application Security Testing (DAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,300+ Authentic Reviews
  • 102+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

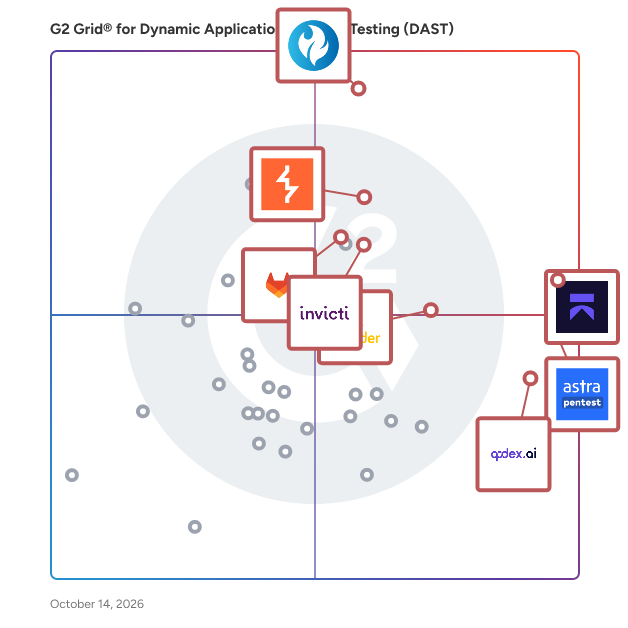
G2 Grid® for Dynamic Application Security Testing (DAST) Software

G2 Grid® for Dynamic Application Security Testing (DAST) Software plotting products by satisfaction and market presence

Highlighted products: HCL AppScan, Aikido Security, Astra Pentest, Burp Suite, Qodex.ai, Intruder, Invicti, and GitLab.

Underlying data: [Grid® JSON](https://www.g2.com/categories/dynamic-application-security-testing-dast/grids.json?focus%5B%5D=hcl-appscan&focus%5B%5D=aikido-security&focus%5B%5D=astra-pentest&focus%5B%5D=burp-suite&focus%5B%5D=qodex-ai&focus%5B%5D=intruder&focus%5B%5D=invicti&focus%5B%5D=gitlab)

Sn1per Professional

Sn1per Professional is an all-in-one offensive security platform that provides a comprehensive view of your internal and external attack surface and offers an asset risk scoring system to prioritize, reduce, and manage risk. With Sn1per Professional, you can discover the attack surface and continuously monitor it for changes. It integrates with the leading open source and commercial security testing tools for a unified view of your data.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Sn1per Professional?

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Sn1per Professional?

Sparrow DAST

Sparrow DAST is a dynamic application security testing solution designed to identify and address security vulnerabilities in web applications. By automatically crawling subdirectories from a web application's URL, it detects potential security flaws, ensuring comprehensive coverage. The solution adheres to global security compliance standards such as OWASP Top 10 and CWE, enhancing software security and quality. Through event-based attack process simulations, Sparrow DAST enables users to quickly understand and mitigate web hacking processes, thereby preventing potential breaches. Key Features: - Automated Vulnerability Detection: Automatically crawls web application URLs to detect security vulnerabilities. - Comprehensive Coverage: Ensures compliance with global security standards like OWASP Top 10 and CWE. - Attack Process Simulation: Reproduces vulnerability attack processes through events, aiding in quick identification and understanding of web hacking methods. - Web-Based User Interface: Eliminates the need for installation, offering easy access via a web browser and centralized management of analysis results. - Powerful Analysis: Utilizes browser event replay technology to detect security vulnerabilities and analyzes open-source web libraries for potential issues. - Integration Support: Overcomes limitations of dynamic analysis through interaction with Sparrow SAST and RASP, providing IAST capability via the TrueScan function. - Detailed Analysis Reports: Provides clear vulnerability information, trends, and detailed reports with analysis methods, results, and solutions for each vulnerability. - Support for Latest Web Technologies: Analyzes web applications using technologies like HTML5 and AJAX, detecting vulnerabilities by reproducing various browser events. - Multi-User Optimization: Allows setting permissions and roles per user, with centralized management and sharing of analysis results among users. Primary Value and User Solutions: Sparrow DAST offers continuous protection of web applications from external attacks by thoroughly analyzing and identifying security vulnerabilities. Its automated detection and comprehensive coverage ensure that applications comply with global security standards, enhancing both security and quality. The solution's user-friendly interface and detailed reporting facilitate quick understanding and remediation of vulnerabilities, empowering organizations to maintain robust and secure web applications.

Who Is the Company Behind Sparrow DAST?

Topscan

Topscan is a continuous security monitoring platform for the DevOps engineer or CTO who owns security among other things. It covers the whole delivery pipeline in one subscription — static analysis in your code, dynamic scanning of live applications and infrastructure, and continuous monitoring of everything you expose to the internet — instead of three separate vendors for SAST, DAST and attack surface management. Perimeter. External infrastructure scanning reports open ports, service versions and known server vulnerabilities matched against CVE databases, with unlimited scheduled rescans. Asset discovery maps the subdomains and hosts you forgot about — the Grafana, the Sentry, the staging box nobody remembers deploying — and new hosts arrive with a review prompt: you confirm ownership before anything is scanned. Attack surface monitoring keeps every exposed service inventoried, and certificate watch catches TLS/SSL expiry weeks early instead of on the Friday night it happens. Applications and code. Web application scanning runs OWASP-class checks against live apps: SQL injection, XSS, exposed admin panels, default credentials, missing headers. Static application security testing covers three kinds of risk in one scan — vulnerable code patterns, committed secrets and keys, and known CVEs in dependencies (software composition analysis) — on every commit, pointing at the exact file and line. Pipeline and cloud. A CI/CD webhook gives you a unique event link to call from the last step of your deploy script: no API keys, no agent, nothing installed on your servers. AWS connects with keys you issue to discover EC2 and Route 53 resources, which are added to monitoring and rescanned when they change. Workflow. Findings are deduplicated and carry severity in your context, CVSS, a first-seen date and an SLA clock with overdue flags. Snooze what you accept, mark false positives and they stop resurfacing, and work through a large backlog in triage mode. Informational findings stay out of the feed and never touch your score. One security score tracks the whole estate over time — the number you show yourself, your CEO or an auditor. Alerts reach the team in Slack or Microsoft Teams and turn into Jira tickets; chat and tracker routing starts on the Advanced plan. Audit and compliance. Auditors ask for evidence of regular scanning and an inventory of what is exposed: scan history with downloadable reports and an exportable asset inventory answer both, which is what most teams use Topscan for ahead of SOC 2, ISO 27001 or a customer security review. Auditor seats are free and read-only, and users are unlimited on every plan. Pricing starts at $129 per month and is published on the site — no demo call required to see it — with a 14-day free trial of the full plan and no credit card. Add a domain and the first map of your perimeter arrives in five to ten minutes.

Average Rating: 4.9/5.0

Total Reviews: 6

Who Is the Company Behind Topscan?

  • Seller: Topscan
  • Year Founded: 2024
  • HQ Location: Dubai, AE
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 83% Small, 17% Medium

What Are Recent G2 Reviews of Topscan?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Traceable AI

Traceable is the industry’s leading API Security company that helps organizations protect their digital systems and assets in a cloud-first world where everything is interconnected. Traceable is the only intelligent and context-aware platform that powers complete API security. Security Posture Management: Traceable helps organizations dramatically improve their security posture with a real time, risk ranked catalog of all APIs in their ecosystem, conformance analysis, identification of shadow and orphaned APIs, and visibility of sensitive data flows. RunTime Threat Protection: Traceable observes user level transactions and applies mature machine learning algorithms to discover anomalous transactions, alert the security team, and block attacks at the user level. Threat management and analytics: Traceable helps organizations analyze attacks and incidents with its API data lake, which provides rich historical data of nominal and malicious traffic. API Security Testing throughout the SDLC: Traceable connects the security lifecycle together with the DevOps lifecycle providing automated API Security tests to be run within the CI pipeline. Digital Fraud Prevention: Traceable brings together its broad and deep data collection over time and cutting edge machine learning to identify fraud across all API transactions

Who Is the Company Behind Traceable AI?

  • Seller: Harness
  • Year Founded: 2018
  • HQ Location: San Francisco
  • Twitter: @HarnessWealth
    1,389 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,832 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 5% Large

What Do G2 Reviewers Say About Traceable AI?

AI-generated summary from verified user reviews

Pros
  • Users find the customer support of Traceable AI exceptional, providing quick and helpful guidance for their inquiries.
  • Users value the exceptional security features of Traceable AI, effectively guarding API endpoints from vulnerabilities.
  • Users find Traceable AI's setup ease impressive, enabling quick deployment and immediate insights into API vulnerabilities.
  • Users appreciate the robust API management features of Traceable AI, enabling effective monitoring and protection of APIs.
  • Users value the flexibility and customization of Traceable AI, enhancing their API security experience significantly.
Cons
  • Users express a desire for more features and functionalities in Traceable AI, highlighting limitations in usability and customization.
  • Users find it challenging to manage false positives in Traceable AI, requiring more effort than expected.
  • Users experience inefficiency in the update process, incurring unnecessary costs and facing challenges with data handling and scaling.
  • Users find the poor documentation of Traceable AI challenging, hindering effective use and requiring additional support.
  • Users highlight the need for improved reporting capabilities, especially for historical data and larger scales.

Trickest Platform

Trickest provides an innovative approach to offensive cybersecurity automation, assets, and vulnerability discovery. The platform combines extensive adversary tactics and techniques with full transparency, hypercustomization, and hyperscalability, making it the go-to platform for offensive security operations. The Trickest platform comes with comprehensive tooling, scripting, managed infrastructure, scaling, ready-to-go solutions, and analytics, serving as a collaborative command center for Offensive Security, Penetration testing, Red teams, Security Analysts, and Security Service providers (MSSPs). What makes us different? Easy customization of logic, inputs, outputs, and integrations, making them adaptable to specific needs and thus producing superior-quality data compared to others. Some of the automation workflows and solutions that our customers deploy and execute: - Attack Surface Discovery - Vulnerability Scanning - Dynamic Application Security Testing (DAST) - Recon/Information Gathering (Passive & Active) - Organization OSINT - CVE scanning - Cloud Scanning - DNS recon & research - Subdomain Enumeration - Subdomain Takeover - Custom Security Automation and Orchestration Main components of the Trickest platform include: Solutions & Analytics - Ready-to-go and transparent solutions for Attack Surface Discovery, Vulnerability Scanning, Dynamic Application Security Testing (DAST), and Open-source intelligence OSINT, offering insight into every step of the process, easy customization, and Analytics on the top. The Builder - Access to 90+ workflow templates, 300+ open-source tools, Bash & Python scripting, CLI for building custom workflows to discover asset, vulnerabilities, scan network & apps, crawl, spider, enumerate, fuzz, bruteforce and much more. Hyperscalability - Whether scanning regional infrastructures with 100s of 1000s of assets or smaller organizational scopes, Trickest supports it all without per-asset costs.

Who Is the Company Behind Trickest Platform?
  • Seller: Trickest
  • Year Founded: 2020
  • HQ Location: Dover, US
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

TruStacks

TruStacks is a software delivery engine that offers standardized, efficient DevOps workflows to help teams ship products faster and more frequently.

Who Is the Company Behind TruStacks?

Vector

Vector is an AI-powered black-box vulnerability scanner. Point it at any web application and it autonomously discovers attack surfaces, tests for vulnerabilities across multiple categories, and generates detailed security reports with proof-of-concept exploits.

Who Is the Company Behind Vector?

we45

AppSec Testing(AST) - Whatever your motivation, a proactive security push or a compliance compulsion, our AST service can help keep your application secure against external threats. Security Automation - Secure your agile Software Development Life Cycle(SDLC) without compromising on quality or time. AppSec Training - Our numerous/variegated training offerings help product teams gain the security understanding necessary to keep their deployments secure. Orchestron - Make Application Security efficient with one of the most integral parts of a modern DevSecOps toolchain - An AVC engine. Threat PlayBook - A (relatively) Unopinionated framework that faciliates Threat Modeling as Code married with Application Security Automation on a single Fabric. Perform Iterative Threat Modeling in an Agile Environment with Threat Playbook.

Who Is the Company Behind we45?

  • Seller: we45
  • Year Founded: 2019
  • HQ Location: San Jose, US
  • LinkedIn® Page: www.linkedin.com
    37 employees on LinkedIn®

Web Application Scanning

A Key Part of Fortra (the new face of HelpSystems) Digital Defense is proud to be part of Fortra’s comprehensive cybersecurity portfolio. Fortra simplifies today’s complex cybersecurity landscape by bringing complementary products together to solve problems in innovative ways. These integrated, scalable solutions address the fast-changing challenges you face in safeguarding your organization. With the help of the powerful protection from Frontline Web Application Scanning and others, Fortra is your relentless ally, here for you every step of the way throughout your cybersecurity journey.

Who Is the Company Behind Web Application Scanning?

  • Seller: Fortra
  • Year Founded: 1982
  • HQ Location: Eden Prairie, Minnesota
  • Twitter: @fortraofficial
    2,773 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,784 employees on LinkedIn®

Web Application Security Testing

Ostorlab is an agentic security testing platform for web applications and APIs. Its AI agents authenticate, navigate multi-step workflows, observe application behavior, and adapt their testing based on what they discover. They follow attack paths across web interfaces and APIs to validate injection vulnerabilities, broken access controls, exposed secrets, insecure configurations, vulnerable dependencies, and business logic flaws—with reproducible evidence. Ostorlab supports APIs defined with OpenAPI and GraphQL, including authenticated and multi-step workflows. Beyond detection, teams can aggregate findings, route them through ticketing integrations, generate fixes with AI Autofix, monitor applications continuously, and validate remediation through retesting.

Who Is the Company Behind Web Application Security Testing?

  • Seller: Ostorlab
  • Year Founded: 2021
  • HQ Location: Middletown, US
  • Twitter: @OstorlabSec
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

XBOW

XBOW is an autonomous, AI-driven penetration testing platform that continuously discovers and validates real, exploitable vulnerabilities in web applications. Unlike traditional DAST scanners that generate noisy results or annual manual pentests that run periodically, XBOW simulates real-world attack behavior and only reports findings that are validated with proof of exploitability. This eliminates false positives and significantly reduces manual triage. Security and AppSec teams use XBOW to increase testing frequency without adding headcount, uncover vulnerabilities that scanners and periodic testing miss, and embed continuous, exploit-backed validation into their development lifecycle.

Who Is the Company Behind XBOW?

  • Seller: XBOW
  • Year Founded: 2024
  • HQ Location: Seattle, US
  • LinkedIn® Page: linkedin.com
    103 employees on LinkedIn®

ZeroNorth

Continuous security delivery fabric for modern enterprise infrastructure.

Who Is the Company Behind ZeroNorth?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024