Best Cloud Detection and Response (CDR) Software - Page 3

How Many Cloud Detection and Response (CDR) Software Products Does G2 Track?

Total Products under this Category: 44

Category Stats (Nov 2026)

  • Average Rating: 4.58/5 (↓0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: UnderDefense MAXI (+0.43%) - Among all products in this category, UnderDefense MAXI recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Cloud Detection and Response (CDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,600+ Authentic Reviews
  • 44+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

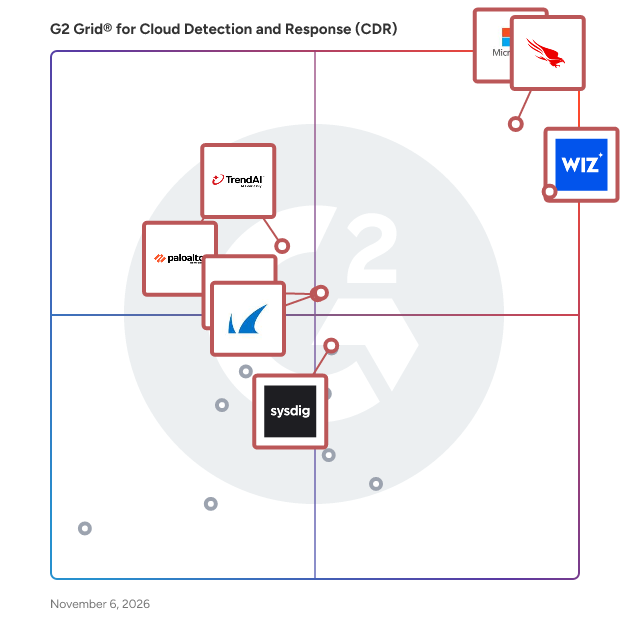
G2 Grid® for Cloud Detection and Response (CDR) Software

G2 Grid® for Cloud Detection and Response (CDR) Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security, Wiz, Cortex Cloud, TrendAI Vision One, Barracuda Managed XDR, Arctic Wolf, and Sysdig Secure.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-detection-and-response-cdr/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=wiz-wiz&focus%5B%5D=cortex-cloud&focus%5B%5D=trendai-vision-one&focus%5B%5D=barracuda-managed-xdr&focus%5B%5D=arctic-wolf&focus%5B%5D=sysdig-sysdig-secure)

Corelight

Corelight's Open Network Detection and Response (NDR) Platform improves network detection coverage, accelerates incident response, and reduces operational costs by consolidating NDR, intrusion detection (IDS), and PCAP functionality in a single solution and by providing security analysts with machine learning-assisted investigations and one-click-pivots from prioritized alerts to the evidence needed to investigate and remediate them. Network Detection and Response platforms monitor and analyze network traffic, delivering telemetry into existing SIEM, XDR, or SaaS-based solutions. Corelight’s platform is unique because our detections and visibility engineering are community driven—with continuous content creation from Zeek®, Suricata IDS, and other Intel communities. And our integration with CrowdStrike XDR enables cross platform (EDR+NDR) analytics. This provides you with the most complete network visibility, powerful analytics, and threat hunting capabilities, and accelerates investigation across your entire kill chain. Corelight also delivers a comprehensive suite of network security analytics that help organizations identify more than 75 adversarial TTPs across the MITRE ATT&CK® spectrum including Exfiltration, Command and Control (C2), and Lateral Movement. These detections reveal known and unknown threats via hundreds of unique insights and alerts across machine learning, behavioral analysis, and signature-based approaches. CORELIGHT PRODUCTS + SERVICES Open NDR Platform Appliance, Cloud, Software, Virtual and SaaS Sensors IDS Fleet Manager Investigator Threat Hunting Platform Smart PCAP Corelight Training CERTIFICATIONS FIPS 140-2

Average Rating: 4.6/5.0

Total Reviews: 20

How Do G2 Users Rate Corelight?

  • Ease of Admin: 9.1/10 (Category avg: 8.9/10)
  • Ease of Use: 8.5/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Quality of Support: 9.1/10 (Category avg: 9.2/10)

Who Is the Company Behind Corelight?

  • Seller: Corelight
  • Year Founded: 2013
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 50% Large, 50% Medium

What Do G2 Reviewers Say About Corelight?

AI-generated summary from verified user reviews

Pros
  • Users value Corelight for its comprehensive security, offering exceptional network event insights and threat detection capabilities.
  • Users praise Corelight for its superior network telemetry, enhancing security detection and event clarity.
  • Users praise Corelight for its effective network telemetry, making security events easy to understand and actionable.
  • Users value the exceptional network security offered by Corelight, enabling easy detection of threats and efficient event analysis.
  • Users value the great network telemetry of Corelight, which simplifies security event analysis and enhances threat detection.
Cons
  • Users find the complex coding of Corelight challenging, especially for those without specialized knowledge.
  • Users find the complex configuration of Corelight difficult, especially for those without specialized knowledge or training.
  • Users find Corelight's complexity challenging, often requiring specialized knowledge and costly training for effective use.
  • Users find the complex setup of Corelight challenging, often requiring specialized knowledge and personalized training.
  • Users find the learning curve steep, making Corelight challenging for novice security analysts to navigate effectively.

What Are Recent G2 Reviews of Corelight?

Vijilan Threat Respond

Vijilan will deploy and implement its fully managed service in record time, and as part of the service, Vijilan will monitor and respond to any threat or suspicious behavior on the network through its technologically advanced SOC and Incident Response Team (IRT) who operate around the clock.

Average Rating: 5.0/5.0

Total Reviews: 2

How Do G2 Users Rate Vijilan Threat Respond?

  • Ease of Admin: 10.0/10 (Category avg: 8.9/10)
  • Ease of Use: 10.0/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Vijilan Threat Respond?

  • Seller: Vijilan
  • Year Founded: 2014
  • HQ Location: Hallandale Beach, US
  • LinkedIn® Page: www.linkedin.com
    79 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Small

What Are Recent G2 Reviews of Vijilan Threat Respond?

What Are G2 Users Discussing About Vijilan Threat Respond?

Wiz CDR

Wiz collects cloud events and alerts from multiple providers, including AWS CloudTrail, Azure Activity Logs, Google Cloud Audit Logs, Amazon GuardDuty, and Google Cloud's Security Command Center. It provides context for the risks identified by the Wiz Security Graph and detects suspicious events and threats via rules continuously updated by Wiz Research. Extend the agentless malware scanning with custom feeds and collect samples, workload logs, and other forensics from cloud workloads. Built-in dynamic scanning validates external exposures, simulating what a potential attacker sees from outside your environment.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate Wiz CDR?

  • Ease of Admin: 10.0/10 (Category avg: 8.9/10)
  • Ease of Use: 8.3/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.3/10)
  • Quality of Support: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Wiz CDR?

  • Seller: WiZ
  • Year Founded: 2016
  • HQ Location: Hong Kong, HK
  • LinkedIn® Page: www.linkedin.com
    8 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Wiz CDR?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Circumvent

Circumvent is a cloud security company with offices in Sydney, and San Francisco, focused on changing the way enterprises manage the security of their cloud infrastructure and applications. Rather than manually triaging individual alerts and assessing business context after the fact, Circumvent’s platform autonomously correlates and triages alerts, delivering accurate prioritization and supervised remediation with one-click human verification. By eliminating alert fatigue and providing source-level fixes, Circumvent helps security teams focus on what matters most—resolving critical risks faster and more effectively.

Who Is the Company Behind Circumvent?

  • Seller: Circumvent
  • Year Founded: 2024
  • HQ Location: North Strathfield, AU
  • LinkedIn® Page: www.linkedin.com
    6 employees on LinkedIn®

CYCL - Managed Cloud Detection and Response

At CYCL, we merge expert cloud knowledge with behavioral AI-based analytics on our Cloud Native Managed CDR platform. By utilizing both agentless and lite agent-based cloud-native technologies, we significantly lighten the load for your security teams. We conduct comprehensive analysis and smart noise reduction, ensuring your attention is utilized only for the alerts and identified risks that truly matter. This allows you to leverage your cloud security investments to their fullest potential without the clutter of additional tools.

Who Is the Company Behind CYCL - Managed Cloud Detection and Response?

enhanced.io

enhanced.io is a channel-only Open XDR SOCaaS built exclusively for MSPs, with 400+ integrations across endpoint, network, cloud, identity and IoT/OT. The service gives MSPs a full security operations center without the cost of building one. A 24/7 SOC team monitors, detects, investigates, and responds to threats across every client environment. A named Fractional Security Director works openly alongside the MSP, joining client calls and quarterly business reviews. enhanced.io replaces MDR and SOCaaS providers and integrates with the partner's existing stack. There is no rip and replace. MSPs keep the client relationship. enhanced.io never sells direct to end clients. The service is particularly well suited to MSPs serving regulated industries like healthcare, legal, and financial services, and IoT/OT-heavy sectors like manufacturing, building management, retail, and education. It is also applicable to clients of any size and shape. Coverage is worldwide.

Who Is the Company Behind enhanced.io?

  • Seller: enhanced.io
  • Year Founded: 2019
  • HQ Location: Edinburgh, United Kingdom
  • LinkedIn® Page: www.linkedin.com
    10 employees on LinkedIn®

Gradient Cyber

​Gradient Cyber’s Managed Extended Detection and Response (MXDR) service offers mid-market organizations comprehensive, 24/7/365 protection across their entire IT environment, including networks, endpoints, cloud infrastructures, Software as a Service (SaaS) applications, and business process applications. By integrating advanced AI/ML-driven analytics with human expertise through our proprietary XDR platform, Quorum™, we ensure rapid detection and neutralization of threats before they can impact operations. ​ Key Features of Gradient Cyber's MXDR Service: - Comprehensive Coverage: Our MXDR solution provides unified detection and response across all critical components of your IT ecosystem, ensuring no blind spots for attackers to exploit. ​ - Proactive Threat Detection: Utilizing a combination of automated tools and human analysis, we identify and mitigate threats in near real-time, significantly reducing the risk of breaches. ​ - Expert-Led Response: With a 10:1 client-to-analyst ratio, our dedicated team of security professionals offers personalized service, acting as an extension of your in-house team to swiftly address and remediate threats. ​ - High Accuracy: Our approach achieves a 99% false positive elimination rate, allowing your IT staff to focus on genuine threats without the distraction of unnecessary alerts. ​ - Scalability Across Industries: Serving clients in over 35 verticals, our MXDR service is tailored to meet the unique security challenges of various industries, ensuring relevant and effective protection. ​ - Robust Infrastructure: Operating from four in-house Security Operations Centers (SOCs) worldwide, we provide continuous monitoring and rapid response capabilities, ensuring global coverage and resilience. ​ - Integrated Compliance Tracking: Our service includes compliance tracking and detailed Situation Reports (SitReps), offering transparency and aiding in regulatory adherence. ​ By choosing Gradient Cyber’s MXDR service, organizations benefit from a seamless blend of technology and human expertise, transforming their cybersecurity posture from reactive to proactive.

Average Rating: 4.8/5.0

Total Reviews: 4

How Do G2 Users Rate Gradient Cyber?

  • Ease of Admin: 10.0/10 (Category avg: 8.9/10)
  • Ease of Use: 9.2/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Gradient Cyber?

Who Uses This Product?

  • Company Size: 50% Small, 25% Medium

What Do G2 Reviewers Say About Gradient Cyber?

AI-generated summary from verified user reviews

Pros
  • Users value the automation capabilities of Gradient Cyber, enhancing security management with proactive detection and intuitive features.
  • Users value the continuous monitoring by Gradient Cyber, which enhances security and reduces the need for daily logins.
  • Users praise the exceptional customer support from Gradient Cyber, feeling like a true partner in security management.
  • Users value the customization options of Gradient Cyber, enabling tailored features that perfectly fit their security needs.
  • Users value the intuitive dashboard customization of Gradient Cyber, enhancing usability and effectiveness across various environments.

What Are Recent G2 Reviews of Gradient Cyber?

Illumio Insights

Illumio Insights brings advanced analytics and security insights, focusing on reducing complexity in risk management and enhancing operational efficiency. Illumio Insights offers powerful tools designed to streamline cybersecurity processes. It provides in-depth visibility into network vulnerabilities and assists organizations in proactively addressing potential threats. With an emphasis on simplicity and efficiency, Illumio Insights supports strategic decision-making by delivering actionable intelligence tailored to business contexts. What are Illumio Insights' key features? Advanced Threat Detection: Provides real-time monitoring of potential security risks, enhancing threat response. Comprehensive Network Visibility: Offers detailed insights into network activities, aiding in identifying weak points. Risk Mitigation Recommendations: Suggests actionable steps to minimize security risks, ensuring informed decision-making. Scalable Architecture: Supports growth by accommodating increasing data volumes and network complexities. What benefits should users look for in reviews? Increased Operational Efficiency: Streamlines security operations by reducing manual interventions. Enhanced Security Posture: Strengthens overall security capabilities through improved threat intelligence. Cost-Effectiveness: Reduces expenses related to data breaches by proactively managing risks. Improved Decision-Making: Facilitates informed decisions with clear and concise security insights. Illumio Insights is adopted across multiple industries such as finance and healthcare to bolster security measures. In finance, it aids in preventing data breaches by providing insights into suspicious activities, while in healthcare, it ensures the protection of sensitive patient data by identifying potential vulnerabilities and recommending mitigation strategies.

Who Is the Company Behind Illumio Insights?

  • Seller: Illumio
  • Year Founded: 2013
  • HQ Location: Sunnyvale, California
  • LinkedIn® Page: www.linkedin.com
    940 employees on LinkedIn®

IntegraTrace

IntegraTrace offers a snapshot of your entire cloud security landscape while using AI to highlight the impacts of changes and run cloud security audits within seconds.

Who Is the Company Behind IntegraTrace?

ion Cloud Security

ion Cloud Security is a cutting-edge Cloud-Native Application Protection Platform (CNAPP) designed to provide real-time security insights, threat detection, and compliance automation for modern cloud environments. Built for speed and scalability, ion helps organizations instantly discover risks, prioritize threats, and enforce security policies across AWS, Azure, and GCP—all from a single, intuitive dashboard. Why Choose ion Cloud Security? 1. Real-Time Cloud Discovery – Instantly identify and secure 100+ resource types across multi-cloud environments. 2. Immediate Exposure Assessment – Onboard cloud accounts seamlessly and get real-time vulnerability insights. 3. Born in the Cloud, for the Cloud – Uncover hidden risks with deep cloud relationship mapping. 4. On-the-Fly Integrations – Effortlessly connect cloud environments with agentless scanning and real-time protection. 5. Instant Threat Detection – Leverage prebuilt detection rules for rapid threat identification and response. 6. Fast Compliance Checks – Meet regulatory standards in minutes with prebuilt compliance templates. Key Features 1. Enhanced Threat Path Visualization Map attack paths to critical assets with interactive cloud relationship graphs. Prioritize risks based on potential impact and exploitability. Accelerate investigations with contextual security insights. 2. Public Cloud Security, Your Way Replace multiple point solutions with a unified CNAPP. Flexible licensing options tailored to your cloud security needs. 3. Comprehensive Cloud Protection 🔹 Posture Monitoring – Gain full visibility into misconfigurations, compliance gaps, and security threats. 🔹 Threat Detection – Detect cloud and hybrid threats with real-time, scalable monitoring. 🔹 Vulnerability Monitoring – Agentless scanning for VMs, containers, and serverless functions. 🔹 Security Data Lake – Analyze security telemetry with a powerful SQL interface. 4. Simplified Cloud Security Operations Single-pane-of-glass dashboard for managing multi-cloud security. Automated risk prioritization to focus on critical threats first. Seamless compliance with prebuilt frameworks (SOC 2, ISO 27001, NIST, GDPR, and more).

Who Is the Company Behind ion Cloud Security?

  • Seller: Cy5
  • HQ Location: Gurgaon, IN
  • LinkedIn® Page: www.linkedin.com
    9 employees on LinkedIn®

Netography Fusion

Netography Fusion delivers a holistic view of all network activity across your multi-cloud or hybrid network, in real-time and at scale. It detects malicious and anomalous activity, such as lateral movement, data harvesting and exfiltration from ransomware without the burden of sensors or agents. Fusion is the fastest way for you to see all network activity. In less than an hour, your cloudops, netops, and secops teams can start seeing all network activity in to, between, and out of your multi-cloud or hybrid network. Data Collection The 100% SaaS Netography Fusion platform begins by collecting VPC flow logs, VNet flow logs, on-prem flow logs, and DNS logs from your multi-cloud or hybrid networks. Fusion’s frictionless architecture eliminates the burden of deploying sensors or agents to collect the data. You simply identify a location of your cloud flow logs and provide credentials for the Fusion platform to ingest the logs, or you can send the logs directly to Fusion from your on-prem network. The metadata Fusion can ingest includes: - Cloud flow logs from all five major cloud providers (Amazon Web Services, Microsoft Azure, Google Cloud, IBM Cloud, and Oracle Cloud Infrastructure) - DNS data from AWS and GCP - Flow data (NetFlow, sFlow, and IPFIX) from routers, switches, and other physical or virtual devices. Orchestrate and Enrich Fusion then orchestrates the cloud flow logs, flow logs, and DNS data into a single dataset, eliminating the need to spend engineering resources to aggregate and normalize the disparate data sources. And, because the metadata represents the “one source of truth” for the network, orchestration ensures that SecOps, CloudOps, and NetOps teams can all take advantage of the same dataset. It enriches the metadata with context attributes from applications and services in the organization’s tech stack, including asset management, CMDB, EDR, XDR, and vulnerability management systems. The context can include dozens of attributes, including asset risk, environment, last known user, region, risk score, security workgroup, type of entity, and vulnerability count. Context transforms the metadata in a network from a table of IP addresses, ports, and protocols into context-rich descriptions of the activities of users, applications, data, and devices. Enriched metadata accelerates any operations teams’ ability to detect and respond to anomalous or compromise activity by eliminating the need to consult other tools or teams to understand the significance of any activity. AI-Driven Analytics Fusion then uses its advanced analytics engine to detect anomalous and malicious activity using Netography Detection Models (NDMs). Created by the Netography Detection Engineering team, NDMs run continuously and search incoming data. Fusion generates an alert when it detects threshold exceptions. Customers have complete flexibility to customize Fusion’s preconfigured detection models as well as create their own models to meet their requirements. Investigate Analysts and investigators can conduct detailed forensic analysis of East/West and North/South activity between and within cloud platforms and cloud to on-prem to see all activity related to a detection. They can quickly pivot between dashboards within Fusion to map the scope and impact of a security incident (including workloads and data sets accessed) or hunt anomalous activity in network traffic to expose the timeline of events. Fusion also enables them to “look back” to see historical activity for up to 12 months, to understand the scope and duration of the activity before detection. Respond The Fusion platform also enables customers to implement a range of response workflows quickly from within the Fusion platform directly or via built-in integrations with a range of technology partners, including EDR and XDR systems, and SIEM/SOAR platforms. Customers can also use Fusion’s APIs to automate workflows with their tech stack as well.

Who Is the Company Behind Netography Fusion?

Primod ADR

Primod is a Cloud Application Detection and Response (CADR) platform for production workloads. An eBPF sensor running in Kubernetes observes what actually executes at runtime, and Primod uses that evidence to detect runtime attacks, give security teams the workload context they need to investigate an incident, and rank vulnerabilities by runtime reachability rather than static severity alone. It also covers cloud security posture management (CSPM). The goal is to reduce the friction between security and engineering teams.

Who Is the Company Behind Primod ADR?

  • Seller: Primod
  • Year Founded: 2025
  • HQ Location: Düzce, Türkiye
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Stream Security

SecOps deserve better than raw cloud telemetry. Most tools patch over noise, ignoring the state of your cloud. We fix the root cause. Stream turns raw cloud telemetry into a stateful real-time model, powering risk-based detection and response.

Who Is the Company Behind Stream Security?

Superna

Who Is the Company Behind Superna?

  • Seller: Superna
  • Year Founded: 2002
  • HQ Location: Kanata, CA
  • LinkedIn® Page: www.linkedin.com
    102 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024