Best Attack Surface Management Software - Page 10

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 189

Category Stats (Sep 2026)

  • Average Rating: 4.6/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+2.02%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,900+ Authentic Reviews
  • 189+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

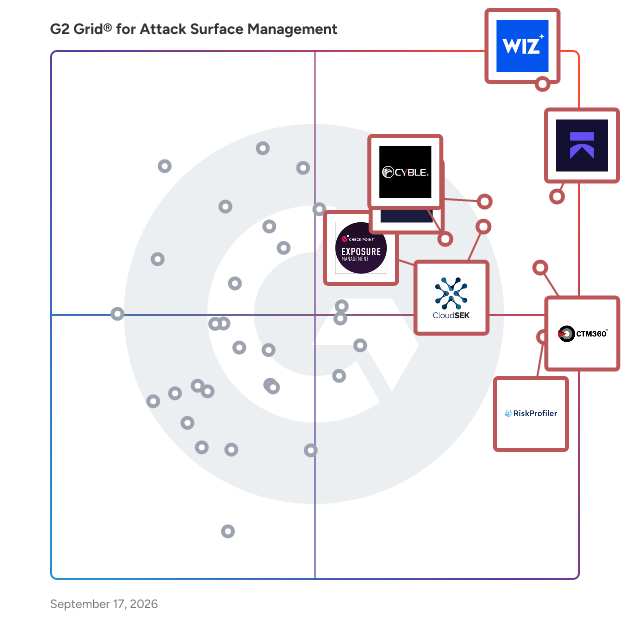
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

Hexiosec ASM

Hexiosec ASM is an attack surface management solution built and supported by ex-UK Government and Defence cyber security engineers in Cheltenham, UK. Using powerful enumeration capabilities, Hexiosec ASM can take a domain, IP, or IP range to scan and discover the internet-connected assets you have visible over the public internet. Once identified, it checks these assets for security vulnerabilities (including KEVs), vulnerable services, at-risk email configurations, valid security certificates, and website security to create a set of risk ratings that will help you prioritise your remediation efforts. The proprietary algorithms our team of engineers have created help Hexiosec ASM find more assets and risks than comparable products in a fraction of the time (average scans are completed within minutes). The passive scanning techniques used by Hexiosec ASM make it ideal for scanning and continuously monitoring your supply chain or helping you perform due diligence on any business without risk to its systems.

Who Is the Company Behind Hexiosec ASM?

  • Seller: Hexiosec Limited
  • Year Founded: 2018
  • HQ Location: Cheltenham, GB
  • Twitter: @hexiosec
    133 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    22 employees on LinkedIn®

Interpres

Interpres is a Threat Informed Defense Surface Management platform that fuses and operationalizes and prioritizes adversarial techniques, tactics, and procedures with your unique threat profile, unique security stack and finished intelligence to identify coverage gaps, prioritize actions, optimize defenses and reduce risk.

Who Is the Company Behind Interpres?

Ionix

Cyberpion’s Ecosystem Security platform enables security teams to identify and neutralize threats stemming from vulnerabilities within the online assets throughout an enterprise’s far-reaching, hyperconnected ecosystem. Modern enterprises leverage countless partners and third-party solutions to enrich online services, improve operations, grow their business, and serve customers. In turn, each of these resources connect with countless more to create a growing and dynamic ecosystem of mostly unmonitored and unmanaged assets. These hyperconnected ecosystems represent a vast new attack surface that falls outside of the traditional security perimeter and enterprise risk management strategies. Cyberpion’s Ecosystem Security platform protects and secures enterprises from this new attack vector. Cyberpion is the only External Attack Surface Management platform that enables organizations to find and eliminate risks in their entire digital supply chain before attackers use them to breach the organization. With Cyberpion, enterprises gain deep visibility and control of hidden risks stemming from Web, Cloud, PKI, DNS misconfigurations or vulnerabilities.

Who Is the Company Behind Ionix?

IONIX Attack Surface Management

IONIX is the attack surface management solution that uses Connective Intelligence to shine a spotlight on exploitable risks across your real attack surface and its digital supply chain. Only IONIX discovers and monitors every internet-facing asset and connection, delivers laser focus into the most important risks to your business, and provides the tools to rapidly remediate exploitable threats and reduce attack surface risk. Global leaders including Infosys, Warner Music Group, The Telegraph, and E. ON depend on IONIX’s machine learning-powered discovery engine, contextual risk assessment and prioritization, and end-to-end remediation workflow to go on the offensive in managing their complex and ever-changing attack surfaces.

Who Is the Company Behind IONIX Attack Surface Management?

  • Seller: IONIX
  • HQ Location: Tel Aviv-Yafo, Tel Aviv District, Israel
  • LinkedIn® Page: www.linkedin.com
    106 employees on LinkedIn®

Jsmon

Who Is the Company Behind Jsmon?

  • Seller: Jsmon
  • Year Founded: 2023
  • HQ Location: Noida, IN
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Kayvrn

Kayvrn is an outside-in security-monitoring platform for businesses that need to understand what an attacker can see from the internet. Enter a domain and Kayvrn runs 57 automated external checks across email security, websites, DNS, cloud services, exposed APIs and related attack-surface signals. No agent, internal credentials or network disruption is required. Results are organised into a plain-English, prioritised report—Fix Now, Fix Soon and Observation—so a business can act without first translating a conventional vulnerability dump. Paid plans add weekly monitoring, scan-over-scan comparison, subdomain discovery, staff-email breach monitoring, CVE and known-exploited-vulnerability alerts, PDF reporting and API access. Initial results are designed to arrive in under 30 minutes.

Who Is the Company Behind Kayvrn?

  • Seller: Conso4s
  • Year Founded: 2019
  • HQ Location: Stevenage, GB
  • LinkedIn® Page: www.linkedin.com
    13 employees on LinkedIn®

KELA Threat Intelligence Platform

KELA’s Unified Threat Intelligence Platform is an all-in-one solution for Cyber Threat Intelligence (CTI), External Attack Surface Management (EASM), Digital Risk Protection Services (DRPS), and Third-Party Risk Management (TPRM), delivering real-time, actionable insights. The platform protects identities, brands, digital exposure, and the supply chain, seamlessly integrating into existing security controls and acting as the first line of defense against cyber threats from the cybercriminal underground. It monitors national risks, critical infrastructure, and supports dark web and cybercrime investigations, helping organizations close security gaps and stay ahead of evolving threats. KELA serves hundreds of customers, including enterprises, MSSPs, law enforcement agencies, CERTs, and government agencies worldwide

Who Is the Company Behind KELA Threat Intelligence Platform?

Lantern

Lantern by MokN is an advanced External Attack Surface Management (EASM) solution designed to help organizations identify, monitor, and secure exposed assets before they become entry points for cyber threats. With real-time asset discovery, vulnerability detection, and proactive alerting, Lantern enables security teams to reduce attack surfaces and prevent breaches. Lantern continuously scans and maps internet-facing infrastructure, detecting misconfigurations, high-risk services, and shadow IT. Its inventory management integrates seamlessly with AWS, Azure, and GCP, ensuring continuous visibility into public-facing assets. Unlike traditional tools that can take days to detect exposures, Lantern provides alerts within 30 minutes, allowing rapid response to security gaps. Built for SOC teams, cybersecurity professionals, MSSPs, and enterprises, Lantern enhances threat intelligence, external risk management, and proactive defense, enabling organizations to stay ahead of evolving cyber threats.

Who Is the Company Behind Lantern?

  • Seller: MokN
  • Year Founded: 2023
  • HQ Location: N/A
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Mandiant Attack Surface Management

Mandiant Attack Surface Management is a cybersecurity solution designed to provide organizations with a comprehensive view of their external digital footprint. By continuously discovering and analyzing internet-facing assets—including cloud resources, applications, and services—ASM identifies vulnerabilities, misconfigurations, and exposures. This proactive approach enables security teams to understand their attack surface from an adversary's perspective, allowing them to prioritize and remediate risks effectively. Key Features: - Continuous and Automated External Asset Discovery: ASM continuously identifies and monitors internet-facing assets across dynamic environments, ensuring up-to-date visibility. - Infrastructure Integrations: The solution supports integrations with cloud and DNS providers, enhancing asset visibility and management. - Intelligence-Informed Active and Passive Checks: Utilizing frontline intelligence, ASM performs both active and passive assessments to validate asset susceptibility to exploitation. - Customizable Scans: Organizations can schedule daily, weekly, or on-demand scans to meet specific security requirements. - Outcome-Based Asset Discovery: ASM allows for tailored asset discovery workflows based on specific outcomes or use cases, enhancing operational efficiency. - Integration Support: The platform is compatible with various Security Information and Event Management , Security Orchestration, Automation, and Response , and ticketing systems, facilitating streamlined remediation processes. Primary Value and Problem Solved: In today's rapidly evolving IT landscape, organizations face challenges in maintaining visibility over their expanding digital environments, which include cloud services, SaaS applications, and remote work infrastructures. This expansion often leads to unknown or unmanaged assets, increasing the risk of cyber threats. Mandiant ASM addresses this challenge by providing continuous, automated discovery and analysis of external assets, enabling organizations to: - Enhance Security Posture: By identifying vulnerabilities before they can be exploited, ASM helps organizations strengthen their defenses. - Mitigate Risks: The solution reduces the attack surface by alerting teams to exposed assets, allowing for timely remediation. - Achieve Comprehensive Visibility: ASM offers a detailed inventory of applications and services within the external ecosystem, ensuring no asset goes unnoticed. By operationalizing threat intelligence and providing actionable insights, Mandiant ASM empowers organizations to proactively manage their attack surface, thereby reducing the likelihood of security breaches and ensuring a robust cybersecurity posture.

Who Is the Company Behind Mandiant Attack Surface Management?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Maphra - Attack Surface Monitoring & Brand Protection

What is Maphra – Attack Surface Monitoring & Brand Protection? Maphra is an advanced, enterprise-grade software platform from DedSec Technologies, purpose-built to provide continuous visibility, analytics and protection of an organisation’s external digital footprint. Its core objective is to identify, monitor and neutralise adversarial exposure across the full attack surface and safeguard brand integrity from threat actors. Key Capabilities Comprehensive Asset Discovery & Monitoring – Maphra scans your externally-facing environment (cloud assets, on-premises systems, SaaS applications, third-party footprint, shadow IT) and builds a unified inventory of your attack surface. dedsecops.com Attack Surface Intelligence – It continuously analyses discovered assets for vulnerabilities, misconfigurations, exposed credentials, leaked data and adversarial paths into your enterprise, providing actionable intelligence rather than raw findings. Brand Protection & Digital Risk Monitoring – Beyond technical exposure, Maphra monitors for brand-impersonation threats (typosquatted domains, phishing infrastructure), leaked customer or employee data, domain abuse and other external risks that can damage brand reputation. dedsecops.com +1 Real-time Alerts and Prioritised Remediation – The platform generates executive-ready dashboards and alerts that prioritise high-risk findings (e.g., exposed credentials, takeover-susceptible domains) enabling security teams and leadership to act swiftly. Business-Aligned Risk Metrics – Maphra translates technical exposure into business risk: visibility over how external vulnerabilities and brand threats map to regulatory, reputational and financial impact, helping the board and c-suite make informed decisions. Why Enterprises Choose Maphra External-First Approach – Unlike tools focused purely on internal networks or cloud workloads, Maphra starts with how an adversary sees your organisation from the outside, reducing the “unknown unknowns” in your ecosystem. Brand & Reputation Focus – In today’s environment where brand trust is a critical asset, Maphra uniquely blends attack surface management with brand-protection capabilities, enabling proactive defence of both technical and reputational risk. Simplified Risk Communication – With board-level metrics and readiness dashboards, Maphra supports CISOs and security leaders in communicating risk beyond the IT team – directly to business stakeholders. Scalable & Enterprise-Ready – Designed for mid- to large-enterprise customers, Maphra integrates with existing security operations, supports large footprints and runs with minimal overhead. https://dedsecops.com

Who Is the Company Behind Maphra - Attack Surface Monitoring & Brand Protection?

Noetic Platform

Noetic’s full-stack visibility and effective controls monitoring empowers enterprises to see the full picture and truly understand significance of relationships between entities, so you can identify gaps and continuously improve efficacy. Find out what you can do with Noetic.

Who Is the Company Behind Noetic Platform?

  • Seller: Noetic Cyber
  • Year Founded: 2020
  • HQ Location: Boston, US
  • Twitter: @NoeticCyber
    124 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,157 employees on LinkedIn®

Nozomi Networks Platform

Nozomi Networks offers highly accurate, actionable intelligence and protection for integrated cybersecurity at scale. The detailed visibility and in-depth insight provided by Nozomi Networks lets users: • See all the OT, IoT, IT, edge and cloud assets on your networks • Pinpoint the cyber threats and vulnerabilities that matter most • Respond quickly to incidents with forensic analysis tools • Manage asset, security and network data in a single platform • Scale cyber and operational resilience across your entire infrastructure

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Nozomi Networks Platform?

  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Nozomi Networks Platform?

  • Seller: Nozomi Networks
  • Year Founded: 2013
  • HQ Location: San Francisco, California, United States
  • Twitter: @nozominetworks
    4,238 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    389 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Do G2 Reviewers Say About Nozomi Networks Platform?

AI-generated summary from verified user reviews

Pros
  • Users highlight the customization features of Nozomi Networks Platform, enhancing their ability to monitor network activities effectively.
  • Users value the effective detection algorithms of Nozomi Networks Platform, which accurately identify intrusions and malicious traffic.
  • Users commend the detection efficiency of Nozomi Networks Platform, effectively identifying intrusions and analyzing traffic patterns.
  • Users value Nozomi's detection algorithms for identifying intrusions and its excellent interface for traffic pattern visualization.
  • Users value the advanced threat detection capabilities of Nozomi Networks, identifying intrusions and malicious traffic effectively.
Cons
  • Users find the Nozomi Networks Platform expensive, yet it aligns with cybersecurity budget constraints against competitors.

What Are Recent G2 Reviews of Nozomi Networks Platform?

Ntrinsec Key Security Automation Platform

Ntrinsec's Key Security Automation Platform is a comprehensive solution designed to eliminate security risks associated with encryption key reuse and poor key management. By integrating with third-party key management systems , hardware security modules , certificate authorities, and major cloud providers, Ntrinsec offers full automation of key lifecycle processes. This ensures that all cryptographic keys adhere to best practices, effectively preventing key compromises. Key Features and Functionality: - Automated Key Lifecycle Management: Seamless integration with existing KMS, HSMs, certificate authorities, and cloud services to automate key generation, rotation, and retirement. - Machine Identity Management: Comprehensive mapping of all keys and host machines to maintain proper key hygiene and identify potential vulnerabilities. - Moving-Target Defense Strategy: Implementation of dynamic defense mechanisms that adapt to evolving cyber threats, outmaneuvering potential attackers. - Anomaly Detection and Remediation: Intelligent policies and automated responses to detect and address anomalies, preventing data breaches before they occur. Primary Value and Problem Solved: Ntrinsec addresses the critical issue of data exfiltration resulting from compromised cryptographic secrets. By automating key management and enforcing stringent key hygiene practices, the platform significantly reduces the risk of key compromise—a leading cause of enterprise data breaches. This proactive approach ensures that organizations can safeguard sensitive information, maintain compliance with security standards, and operate with confidence in increasingly complex digital environments.

Who Is the Company Behind Ntrinsec Key Security Automation Platform?

Who Uses This Product?

  • Company Size: 100% Medium

Observatory ASM

External Attack Surface Management (EASM) is the process of continuously discovering, monitoring, evaluating, prioritising and remediating possible entry points within an organisation’s IT infrastructure that could be susceptible to an attack. Our platform combines some of the most comprehensive scanning and data sources on the internet to provide a complete picture of your exposed enterprise technology estate.

Who Is the Company Behind Observatory ASM?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026