Best Application Security Posture Management (ASPM) Software - Page 3

How Many Application Security Posture Management (ASPM) Software Products Does G2 Track?

Total Products under this Category: 50

Category Stats (Nov 2026)

  • Average Rating: 4.53/5 (↓0.02 vs Oct 2026) The average rating of products in this category, based on all submitted ratings

Last updated: November 01, 2026

How Does G2 Rank Application Security Posture Management (ASPM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,300+ Authentic Reviews
  • 50+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

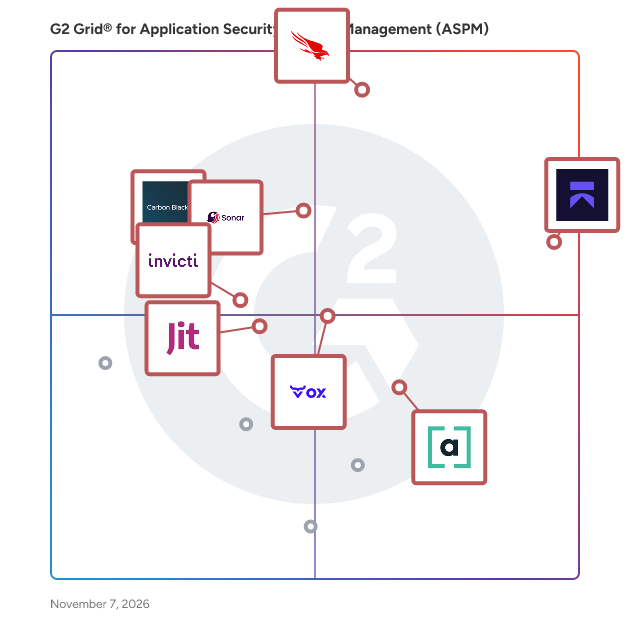
G2 Grid® for Application Security Posture Management (ASPM) Software

G2 Grid® for Application Security Posture Management (ASPM) Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, CrowdStrike Falcon Cloud Security, SonarQube, OX Security, Arnica, Invicti, Jit, and Carbon Black App Control.

Underlying data: [Grid® JSON](https://www.g2.com/categories/application-security-posture-management-aspm/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=sonarqube&focus%5B%5D=ox-security&focus%5B%5D=arnica&focus%5B%5D=invicti&focus%5B%5D=jit&focus%5B%5D=carbon-black-app-control)

Boman.ai

Boman.ai is a plug-n-play DevSecOps product, that can bring continuous application security to the DevOps pipeline. It brings SAST(Static Application Security Testing), DAST(Dynamic Application Security Testing), SCA(Software Composition Analysis), and Secret Scanner to the CICD pipeline. It is powered by ML to remove false positives and noise Can integrate with existing application security tools It offers a vulnerability management system and complete visibility of application security under a single platform. Can create compliance reports Can integrate with Jira and Developer workflows. The scans happen at the customer's CICD, Boman.ai doesn't upload any customer code anywhere.

Who Is the Company Behind Boman.ai?

Conviso

The Conviso Platform is a complete Application Security Posture Management (ASPM) solution that centralizes visibility, correlation, and prioritization of vulnerabilities across the software development lifecycle. It integrates with your existing SAST, DAST, SCA, IaC, and CI/CD tools, automates triage, and provides a unified view of risk — helping security and development teams work together to reduce complexity and strengthen AppSec maturity.

Who Is the Company Behind Conviso?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Dam Secure

Dam Secure is an AI-native application security platform for teams that build software with AI coding agents. It enforces security rules across the development lifecycle, including agentic planning, the local development environment, and CI/CD, before code ships to production. The platform reviews an organization's existing codebase and generates security rules in plain English, tailored to that codebase's own patterns rather than generic policy. These rules are enforced across every developer, AI agent, and repository. At the planning stage, Dam Secure reviews plans co-authored by developers and AI agents. In the dev environment, it checks AI-generated code before it's committed. In CI/CD, it checks pull and merge requests before they reach production. Dam Secure is built to catch business logic flaws in AI-generated code that traditional tools miss, using codebase context to reduce false positives. It integrates with common AI coding tools (including Cursor, Claude Code, and GitHub Copilot) and version control platforms (Bitbucket, GitHub, GitLab), and keeps a persistent record of security context across the workflow.

Who Is the Company Behind Dam Secure?

Dazz

The Dazz Unified Remediation Platform maps your code-to-cloud environment and overlays it with everything you need to know about security.

Who Is the Company Behind Dazz?

  • Seller: Dazz
  • Year Founded: 2021
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    56 employees on LinkedIn®

Enablon Incident Management

Who Is the Company Behind Enablon Incident Management?

  • Seller: Wolters Kluwer
  • Year Founded: 1987
  • HQ Location: Alphen Aan Den Rijn, The Netherlands
  • LinkedIn® Page: www.linkedin.com
    22,401 employees on LinkedIn®
  • Ownership: AMS:WKL
  • Total Revenue (USD mm): $4,603

Heeler

Heeler empowers application security teams to shift left with the context they need to reduce noise, accelerate remediation, and move beyond traditional vulnerability management. By combining ASPM, SCA with static and runtime context, and runtime threat modeling, Heeler transforms AppSec programs from reactive firefighting to proactive, scalable security. How Heeler Helps AppSec Teams • Reduce Noise: AppSec teams and developers are drowning in findings. Heeler delivers unified code, runtime, business and security context, reducing alert noise by up to 95%, so teams can focus on critical issues and fix what matters most. • Fix Remediation: Remediation is broken. Most effort is spent reaching a fix—not implementing it. Heeler automates the remediation lifecycle, cutting effort and time, enabling AppSec teams to scale alongside engineering. • Move Beyond Vulnerabilities: With Heeler, continuous runtime threat modeling becomes a reality. Decompose running applications, track changes, compare deployments, and stop risks in real time—all before they reach production. Why Heeler is Essential Modern applications are more complex and dynamic than ever, expanding attack surfaces and making end-to-end security modeling nearly impossible without the right tools. Heeler bridges this gap, addressing the root causes of unscalable AppSec programs: • Lack of Context: Disparate data silos make understanding application behavior and identifying risks challenging. • Labor-Intensive Processes: Without unified context, security efforts are manual, unscalable, and push risk identification too far right. • Firefighting Mode: Security and engineering teams are trapped addressing too many findings and often focus their time on the wrong threats, leaving no bandwidth for secure-by-design initiatives. Key Capabilities • ProductDNA (Unified Context): Automates a real-time service catalog, mapping changesets to deployments and modeling every service with integrated code, runtime, business, and security context. • Runtime Threat Modeling: Enables continuous threat modeling with tools to decompose applications, track changes, compare deployments, and uncover risks in real time. • ASPM: Heeler reduces alert noise by up to 95% and automates remediation workflows, scaling security seamlessly with engineering demands. • SCA with Static and Runtime Context: Combines static and runtime data with business and deployment context, delivering next-gen SCA that prioritizes what matters, strengthens security, and simplifies AppSec workflows. Heeler ensures AppSec teams and developers have the context they need to shift left and build secure-by-design applications—effortlessly.

Who Is the Company Behind Heeler?

IRIS

CodeEye's IRIS is a next-generation application security posture management (ASPM) platform, offers an all-in-one solution with real-time, AI-powered vulnerability and threat detection, correlation, prioritization, and remediation, easing the tension between time-to-market and risk mitigation. How it Works? Unlike traditional ASPM Solutions, IRIS detects vulnerabilities within the product development lifecycle and application infrastructure, while simultaneously providing continuous penetration testing and attack surface management to production environments. IRIS detects, correlates, provides risk-based analysis, and prioritizes application security findings in real time with automated workflows for remediation – all within one platform. IRIS seamlessly integrates with your tools, pipelines, and workflows, and supports your favourite languages. Unlock the Benefits: 1) Centralize detection, prioritization, and remediation of application threats and vulnerabilities. 2) Real-time actionable insights. 3) Establish resilient DevSecOps processes based on risk management. 4) Implement automated workflows to accelerate the identification and resolution of application risks. 5) Adopt a straightforward licensing model. 6) Ability to measure the effectiveness of your application security program. 7) Deploy within 24 hours with simplicity and ease of operation. 8) Built-in policy compliance measures. Next-Gen ASPM Managed Service In today's digital landscape, organizations grapple with deciphering and prioritizing the criticality of code and application related threats and vulnerabilities. The scarcity and expense of specialized talent capable of bridging the gap between DevOps and SecOps exacerbates this challenge. CodeEye's expertise in Application Security provides a Continuous AppSec Partner, accelerating program maturity with expert guidance and advanced technology. Our IRIS Managed Service centralizes application risk management, helping you define compliance measures and policies for prioritization and remediation, ensuring you grasp and address program risk in real-time. Key Features - Static Application Security Testing (SAST): Scans your source code for security risks before an issue goes to production. - Software Composition Analysis (SCA): Continuously monitors your code for known vulnerabilities and other security risks. - Container Scanning: Scans your container in real time for packages that contain security threats and vulnerabilities. - Dynamic Application Security Testing (DAST): Dynamically tests your production applications for vulnerabilities through simulated attacks. - Attack Surface Management (ASM): Continuously identifies, monitors, and manages external internet-connected assets for potential attack vectors and exposures. - Risk and Compliance: Continuously evaluates regulatory and internal security policy compliance using real-time and historical reporting. Vendor of Record Award CodeEye's IRIS is recognized as a Vendor of Record by the Ministry of Government and Consumer Services for IT Security Products In 2024, NIST updated its Cyber Security Framework (CSF) with significant implications for security by design and secure SDLC. Our Risk and Compliance module supports compliance with NIST CSF 2.0 throughout the software development lifecycle. Gain a comprehensive view of various scanning modules aligned with the CSF's five core functions: Identify, Protect, Detect, Respond, and Recover. Our Difference: An all-in-one platform with straight forward licensing and seamless integration. Your Results: A tool that works with your existing tools and workflows, providing security without hidden costs or complexities. Our Difference: Continuous penetration testing and attack surface management. Your Results: Identify and close gaps before an attacker exploits them across your ever-changing attack surface. Our Difference: Quick and Easy Deployment Your Results: Security monitoring and testing within 24 hours, without extensive setup or training. Our difference: Built-in risk and compliance policy module Your Results: Ensure regulatory and internal compliance with built-in policy measures aligned with industry standards like NIST CSF 2.0. Our Difference: Automated Workflows for remediation. Your Results: Rapid risk mitigation, reducing the time, effort and cost of finding and fixing vulnerabilities to ensure continuous protection. Our Difference: Real-Time, AI-powered vulnerability Your Results: Immediately identify and address security threats with precise, actionable intelligence. Our Difference: Threat and vulnerability detection, correlation, and risk-based analysis. Your Results: Simplified security operations where critical vulnerabilities are addressed first.

Who Is the Company Behind IRIS?

  • Seller: CodeEye
  • Year Founded: 2015
  • HQ Location: Toronto, CA
  • LinkedIn® Page: www.linkedin.com
    18 employees on LinkedIn®

Kodem Security

Kodem is an application security platform powered by Runtime Intelligence. Kodem secures the software supply chain and the underlying cloud infrastructure throughout its lifecycle from development to production.

Who Is the Company Behind Kodem Security?

Legit Security

Legit Security provides an application security posture management platform that secures application delivery from code to cloud and protects an organization's software supply chain from attacks. The platform’s unified application security control plane and automated SDLC discovery and analysis capabilities provide visibility and security control over rapidly changing environments and prioritize security issues based on context and business criticality to improve security team efficiency and effectiveness.

Who Is the Company Behind Legit Security?

Oxeye Application Security Platform

Oxeye is an application security solution that was developed to address the unique architecture of cloud native applications. We combine static analysis with runtime flow tracing and infrastructure analysis. Using this multilayered approach, we provide a contextual analysis of vulnerabilities, and prioritize them based on their severity. For greater insights, we report whether third party packages are loaded or not, show infrastructure configuration, and graphically show users the vulnerable flow from the internet to a particular line of code, for quicker remediation. With Oxeye, false positives, and false negatives, become a thing of the past. Installation generally takes less than 5 minutes, and does not require changes to the code or the deployment of any software packages. All that’s required is the deployment of a container within your environment. Once running, Oxeye will automatically scan the environment and provide all of the analysis on its own.

Who Is the Company Behind Oxeye Application Security Platform?

Proscan

Proscan is a unified application security platform designed to help organizations streamline the management of their security tools. By integrating multiple standalone solutions into a single cohesive experience, Proscan provides comprehensive security visibility across the entire software stack. This platform replaces the complexity of managing various tools for static analysis, dynamic testing, and dependency scanning, allowing teams to focus on building secure applications without the hassle of juggling disparate systems. The platform is particularly beneficial for security teams, developers, and engineering leaders who require a consolidated view of application security risks. Proscan combines nine specialized security scanners, including Static Application Security Testing (SAST), which analyzes source code in over 30 programming languages using advanced detection methods. Dynamic Application Security Testing (DAST) further enhances security by testing live applications, identifying vulnerabilities that may only become apparent during runtime. Additionally, Software Composition Analysis (SCA) evaluates open-source dependencies across 196 package ecosystems, helping organizations detect known vulnerabilities before they can impact production environments. Proscan's capabilities extend beyond code analysis. It includes scanning for hardcoded secrets, misconfigurations in Infrastructure-as-Code, and vulnerabilities in container images. The platform also offers API security testing that validates endpoints against the OWASP API Security Top 10, ensuring robust protection for applications that leverage APIs. For organizations developing AI-powered applications, Proscan features a dedicated AI and LLM security scanner that identifies potential risks associated with prompt injections and other vulnerabilities, utilizing over 4,600 techniques mapped to the OWASP LLM Top 10. Artificial intelligence plays a crucial role in enhancing Proscan's efficiency and accuracy. The platform employs machine-learning algorithms to reduce false positives and prioritize vulnerabilities based on their potential impact. This intelligent approach allows teams to focus on the most critical security issues while providing clear explanations and actionable remediation guidance. Proscan integrates seamlessly into existing development workflows, offering IDE plugins and native CI/CD integrations that ensure security checks are part of the development process without causing disruptions. Compliance readiness is another key feature of Proscan, as it generates audit-ready reports aligned with major security standards, including OWASP Top 10, PCI DSS, HIPAA, and GDPR. This automated evidence collection simplifies the compliance process, providing organizations with the necessary documentation in various formats. Proscan is designed for security teams looking to consolidate fragmented toolchains, developers needing quick feedback, and managed security service providers managing multiple client environments, making it a versatile solution for modern application security challenges.

Who Is the Company Behind Proscan?

Rezliant Maestro

Rezliant Maestro is the AI security engineer for financial technology applications and regulated industries, saving 2 months in engineering costs and accelerating enterprise procurement. It is an autonomous platform that identifies and remediates vulnerabilities in payment gateways, ledger databases, and enterprise APIs. Maestro integrates into CI/CD pipelines, enabling adoption without disrupting existing workflows. The platform discovers ledger logic flaws, transaction vulnerabilities, and compliance exposures related to PCI-DSS and SOC 2 standards. Using reachability-based risk triaging, Maestro prioritizes and fixes vulnerabilities based on exploitability.

Who Is the Company Behind Rezliant Maestro?

RiskApp

RiskApp proves your app is secure — before and after it ships

Who Is the Company Behind RiskApp?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024